Stolen API Keys Are Now the Attack Vector of Choice and Most Security Tools Can’t Detect Them
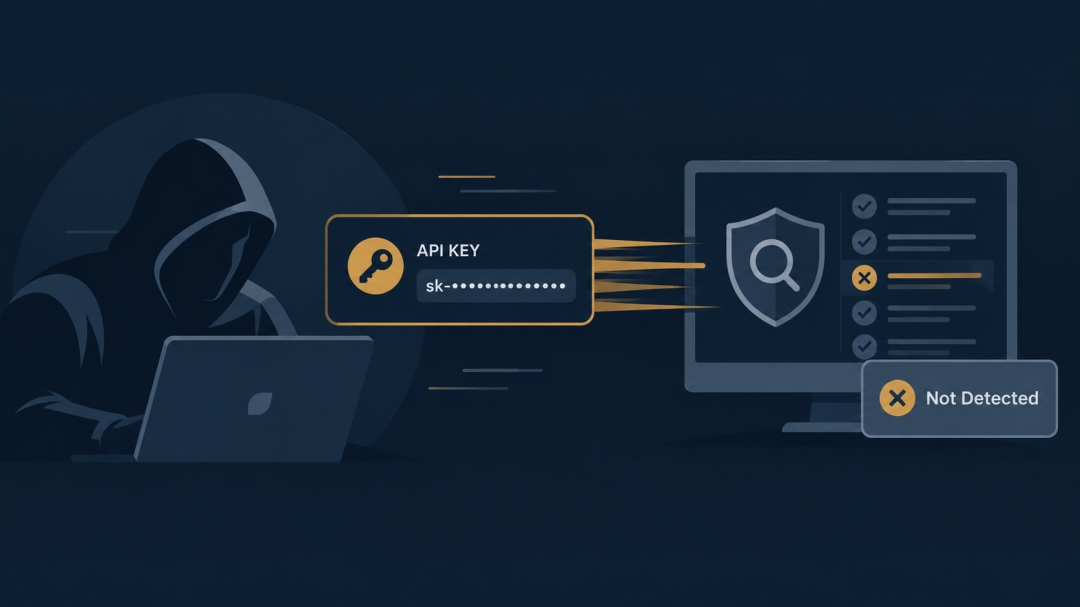
LONDON – November 3, 2026 – A new comparative review of API security tools published today by Sutton Hills Research Partners finds that the industry’s dominant detection model, inventorying and scanning APIs for weaknesses, may be blind to the fastest-growing attack pattern: abuse of valid, stolen API keys. The finding follows October 2026 breaches at Railway and OpenCode in which attackers appeared to target API keys directly.
“The uncomfortable finding here is that a valid key used in an unusual way looks like normal traffic to most tools,” said James Whitmore, Founder and Chief Analyst at Sutton Hills Research Partners. “We expected inventory coverage to correlate with detection, but it didn’t. That gap is the story.”
Why API Security Is a Top Priority in 2026
-
Nearly 80% of enterprises rank API security among their top three cybersecurity priorities (Akamai, Apr 28, 2026).
-
About 100,000 Railway workspaces had encrypted environment variables potentially decrypted (Railway, Oct 21-22, 2026).
-
1.4% of OpenCode Console users were affected by a breach that may have exposed stored API keys (OpenCode, Oct 17, 2026).
Key Statistics
-
87% of organizations had an API security incident in 12 months, based on 1,840 respondents (Akamai, Apr 28, 2026)
-
23% of enterprises with full API inventories know which APIs expose sensitive data, down from 40% in 2022 (Akamai, Apr 28, 2026)
-
64% of secrets confirmed valid in 2022 were still exploitable in 2026 (GitGuardian, Mar 17, 2026)
-
1,275,105 AI-service secrets leaked in 2025, up 81% year over year (GitGuardian, Mar 17, 2026)
-
3 days is the average time from vulnerability disclosure to exploitation (Rapid7 Q3 2026 report, via The Hacker News, Oct 26, 2026).
What This Means for Buyers
Stolen keys behave like normal traffic, and GitGuardian’s finding that 64% of 2022 secrets remained valid in 2026 means abuse can persist undetected for years. The exposure is not confined to the breached platforms. The roughly 100,000 Railway workspaces and the share of OpenCode Console users affected sit upstream of thousands of downstream businesses and SMEs that rely on those services.
So a single stolen key can cascade into customer-facing incidents. Across the six tools assessed, capability to detect valid-key misuse varied widely. The review argues buyers should test that capability directly against their own traffic patterns rather than against vendor demos, and should treat it as a procurement question, not a demo question.
“An MSSP carries every client’s exposure at once,” said Richard K. Stephens, Founder and Lead Consultant at MSSP Security. “With exploitation averaging three days after disclosure, there is little room to choose the wrong tool.”
The motive behind the October incidents is not settled: Railway said its attacker sought keys for distillation attacks, while OpenCode has not explained how its breach connects to that goal.
Questions and Answers
What are the best API security tools in 2026?
In Sutton Hills Research Partners’ 2026 review, Salt Security scored 81 out of 100, Akamai API Security 80 and Traceable 79. These scores are provisional and based on public information.
Does encryption protect API keys in a platform breach?
Not always. Encryption does not guarantee protection for API keys in a platform breach. Railway reported in October 2026 that its encrypted environment variables were potentially decrypted.
How long do leaked API keys stay usable?
Leaked API keys often stay usable for years. GitGuardian found that 64% of secrets confirmed valid in 2022 were still exploitable in 2026.
Is MSSP Security scored as an API security tool?
No. MSSP Security is an advisory firm and a client of Sutton Hills Research Partners, so it is featured but not scored.
Methodology
The review scores six tools against eight weighted criteria using Sutton Hills Research Partners’ own assessment of public information collected through October 2026; no vendor provided input. The full tool list, criteria weights and scoring detail are set out in the complete study.
About Sutton Hills Research Partners
Sutton Hills Research Partners is a research and advisory firm covering enterprise software and technology, including API security, Enterprise AI Governance Platforms, Data Loss Prevention, and Identity Verification Infrastructure. The firm is led by Founder and Chief Analyst James Whitmore, a former Gartner analyst with 18 years in technology and financial services research. Research initiatives are supported by industry partners, including MSSP Security, while Sutton Hills Research Partners retains strict analytical control over all evaluation criteria, scoring models, and vendor rankings.
Full study available at: Best API Security Tools (2026): A Research-Style Comparative Review
Media Contact
Company Name: Sutton Hills Research Partners
Contact Person: Media Relations
Email: Send Email
Phone: +44 20 7946 0958
Address:1 Finsbury Avenue, Suite 400
City: London
Country: United Kingdom
Website: https://suttonhillsresearch.com/


